Vulnerability Assessment Report: Public Database Server
Overview
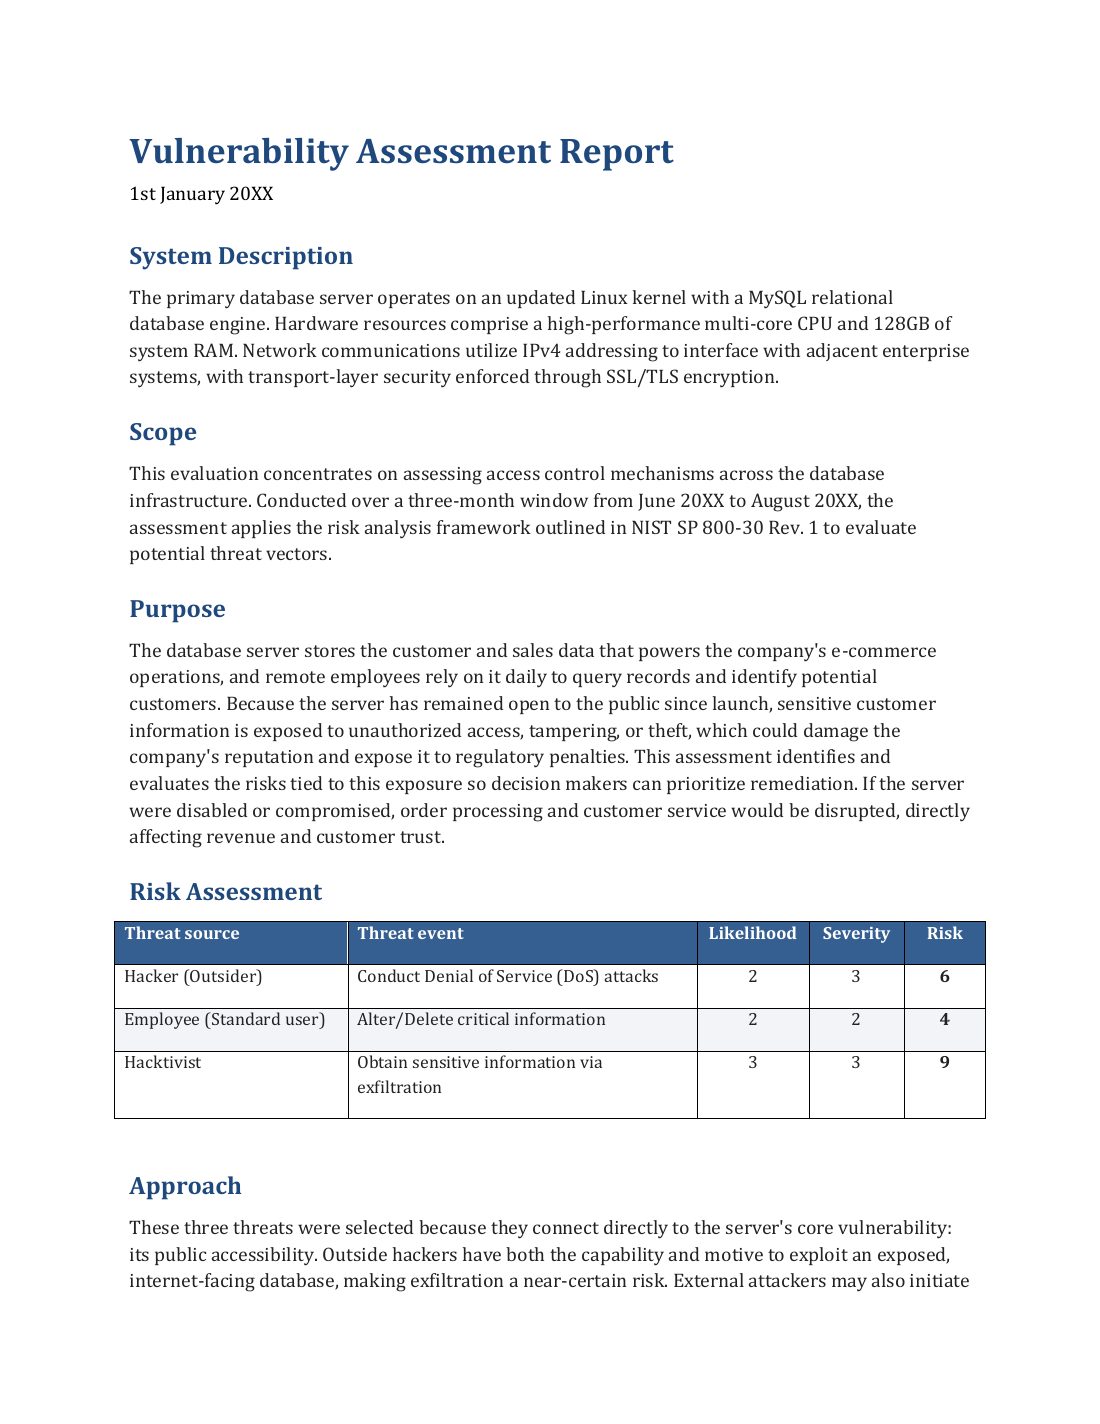
The company’s customer and sales database had been open to the public since launch. This assessment focused on its access control mechanisms, over a three-month evaluation window, using the risk analysis method in NIST SP 800-30 Rev. 1.
What I did
- Documented the system (Linux, MySQL, SSL/TLS) and the business purpose of the server.
- Identified threat sources and events, then scored them by likelihood and severity.
- Recommended remediation to restrict access and protect sensitive data.
The deliverable