Incident Report: SYN Flood on a Sales Web Server
Overview
Customers were getting connection timeout errors on the company’s sales website.
What I did
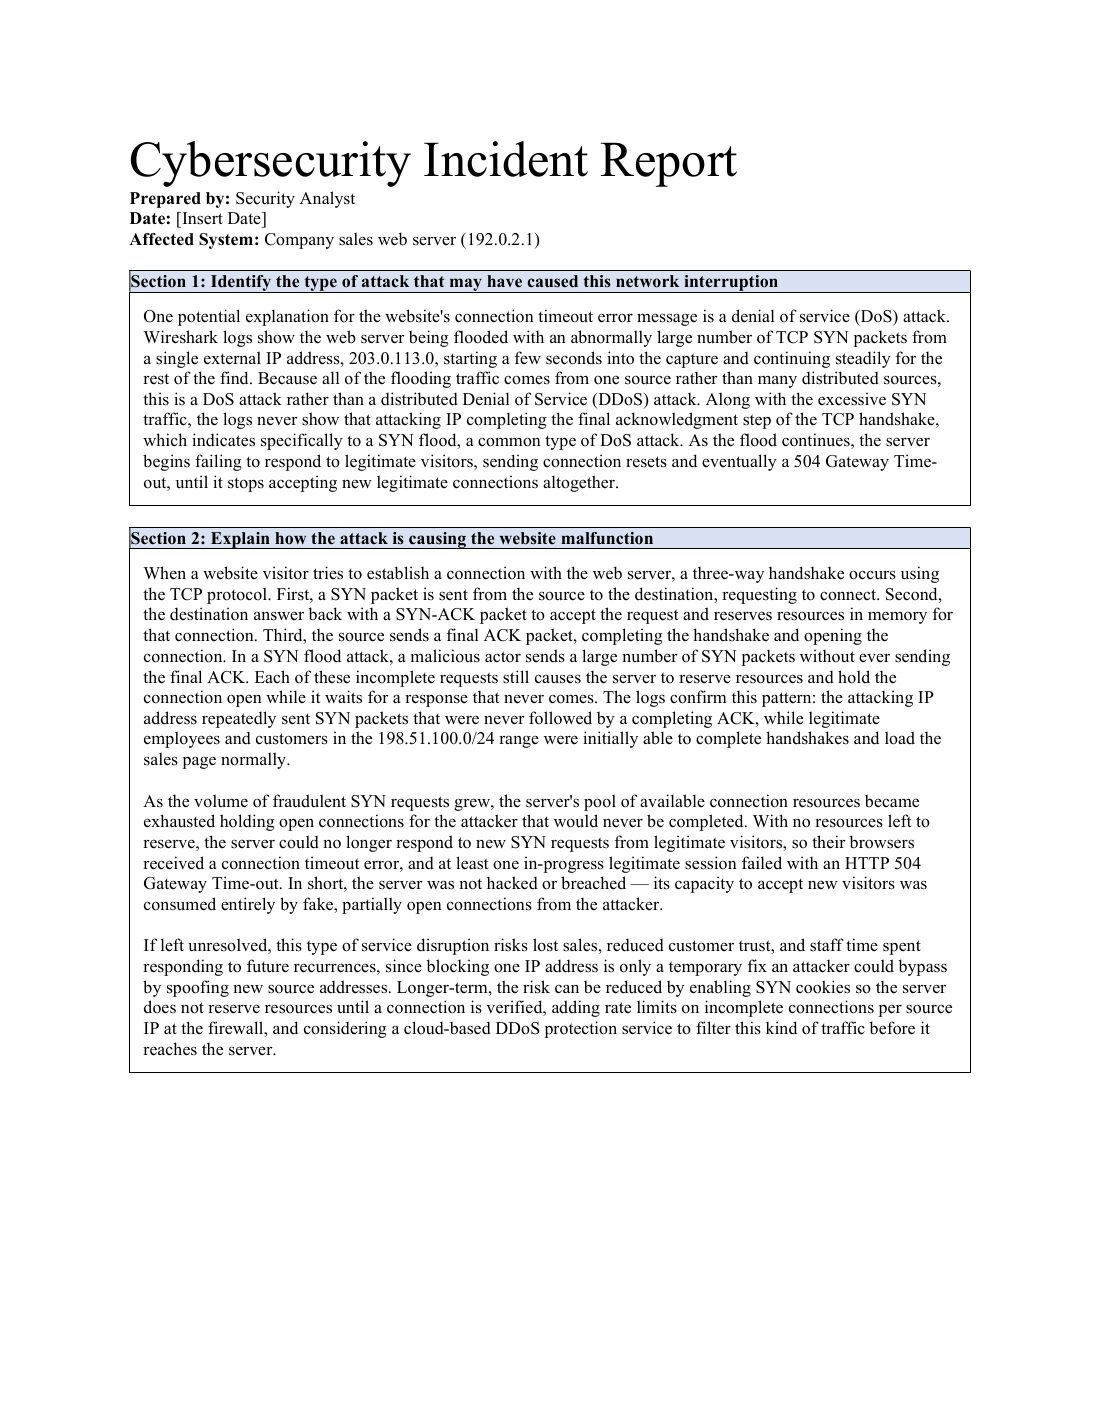
- Found an abnormally large number of TCP SYN packets from a single external IP in the Wireshark logs.
- Classified it as a DoS (single source) rather than a DDoS, and specifically a SYN flood, because the attacker never completed the TCP handshake.
- Explained how the flood exhausted the server’s resources and caused the timeouts.
The deliverable