Incident Report: ICMP Flood DoS
Overview
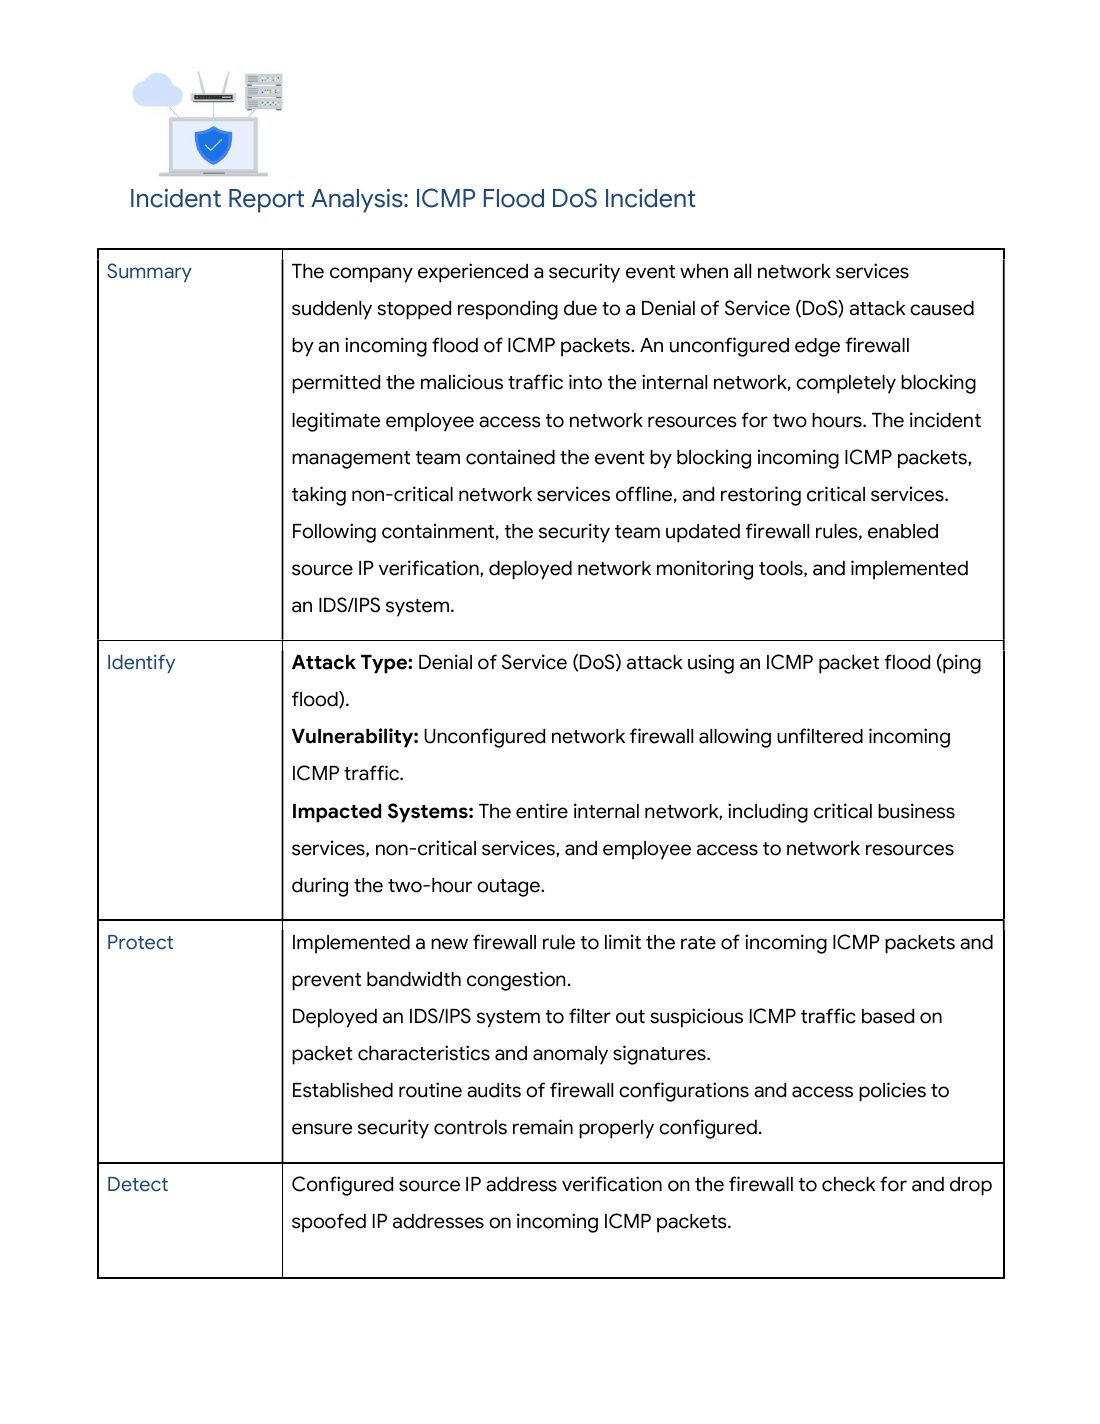
All network services stopped responding for two hours after an ICMP packet flood passed through an unconfigured edge firewall.
What I did
- Identify: pinpointed the attack type (ICMP ping flood), the vulnerability (unfiltered incoming ICMP) and the affected systems.
- Protect / Detect / Respond / Recover: documented containment (blocking ICMP, taking non-critical services offline) and follow-up controls: new firewall rules, source IP verification, network monitoring and an IDS/IPS.
The deliverable